
GUARDRAILS AND AUTOMATION
The agent control checklist for leadership teams
For CEOs, COOs, and security leaders who answer for what AI agents do
Most organisations govern artificial intelligence (AI) with a written policy. An AI agent does not read a policy. It works within whatever limits the systems around it enforce.
Agents now write code, draft documents, and open change requests through the same systems your employees use. Few leadership teams can say which of their controls a system enforces and which depend on people following a rule. Okta surveyed 306 security executives in 2026. Fewer than half were confident they could identify all the AI agents in their environment.¹
This checklist gives you ten yes or no questions to put to the people who run your systems. Each one comes from a problem we met while putting agents to work on our own engineering and operations, and you do not need a technical background to use it.
What is inside
Key terms in plain language
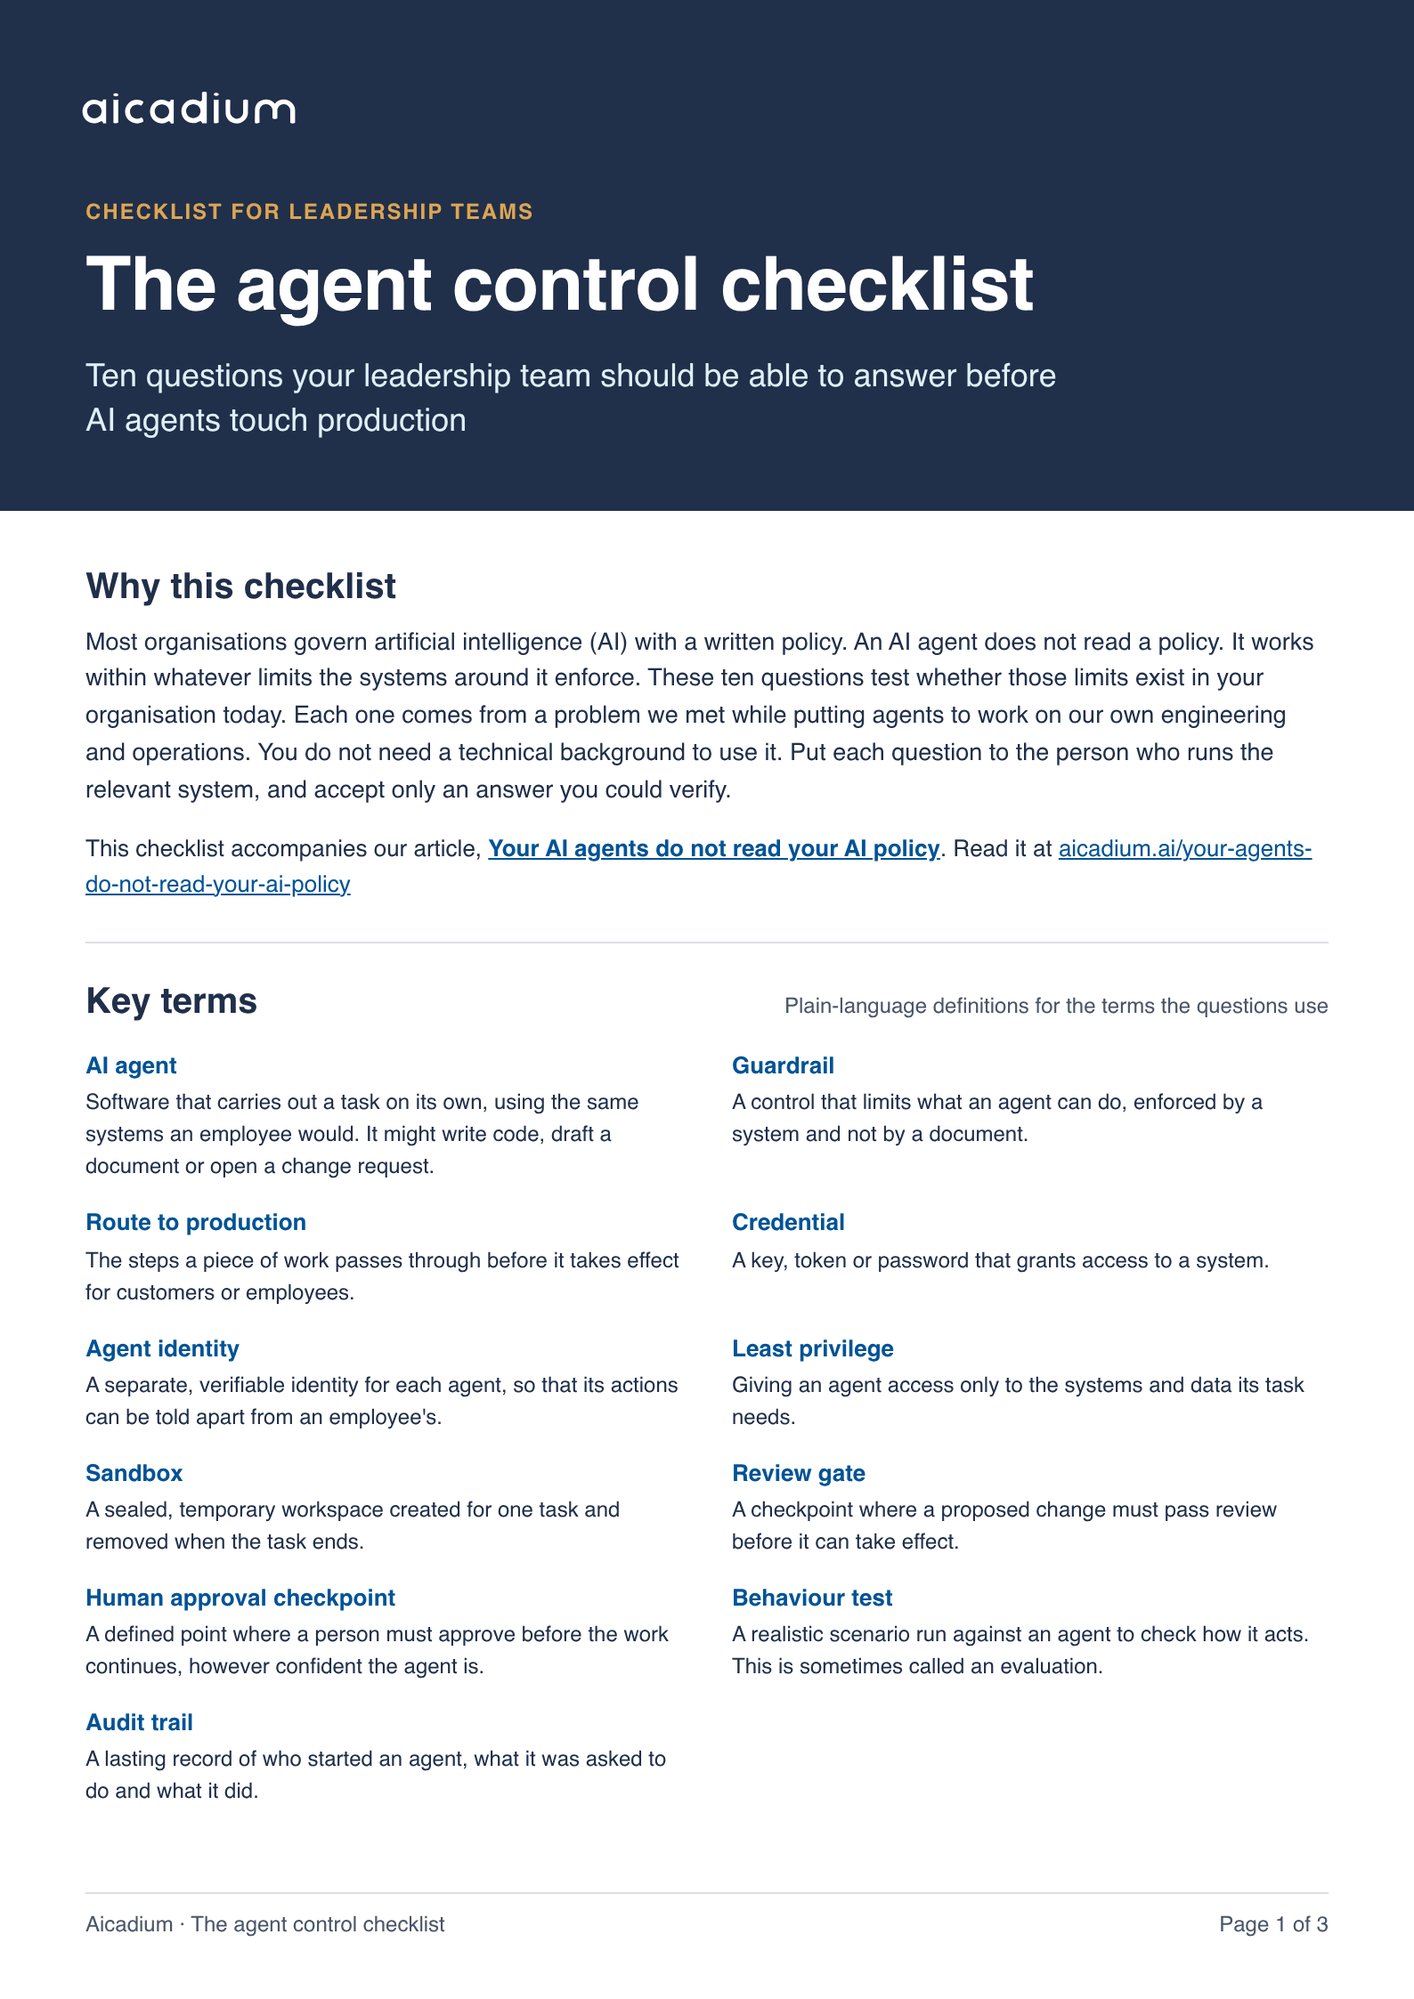
Eleven short definitions, from guardrail to audit trail, so that everyone on the leadership team reads the questions the same way.
Ten questions in five groups
The groups cover visibility and ownership, access and credentials, review and approval, testing, and evidence. A yes counts only when a system enforces the control.
A score and a place to start
Score one point for each yes. Three score bands show whether your controls are enforced by systems or rely mainly on written policy, and which "no" answers to address first.
Read the blog post
The companion article, Your AI agents do not read your AI policy, explains why a written policy cannot govern AI agents and how each control in this checklist works.